HOL Guard
Apply local approval rules before AI agents take risky actions
Discover and govern AI agent activity across company endpoints
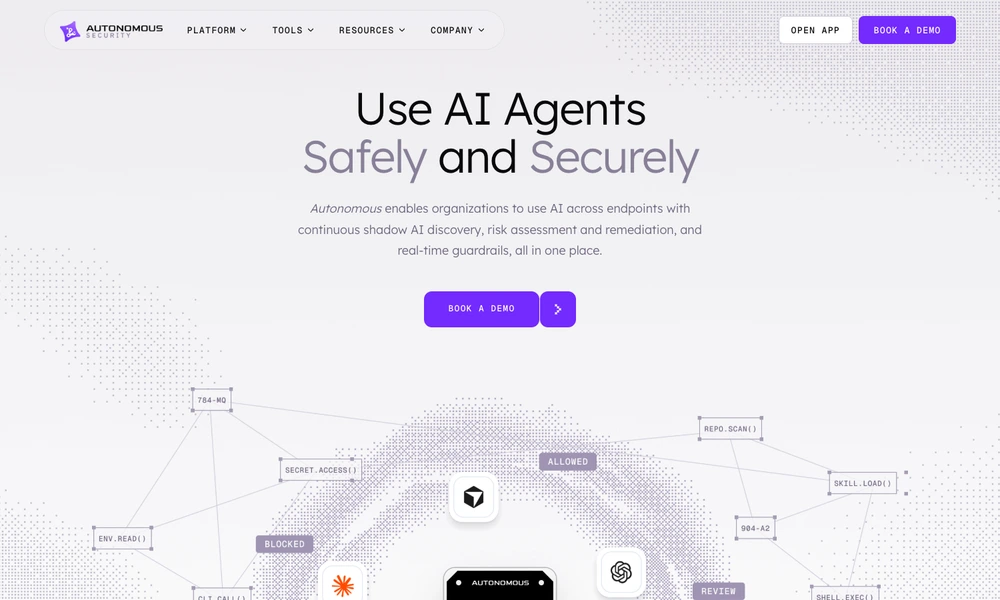
Autonomous Security helps organizations understand and control the AI agents, applications, models, and related components running across their endpoints. It builds an inventory of AI usage and examines MCP servers, skills, permissions, and credentials for potential risks. Security teams can define which tools and activities are approved, restricted, or prohibited.
Runtime controls apply those policies while agents work, with options to block unauthorized commands and manage access to company systems and data. The platform also connects findings and activity with existing security infrastructure, including identity and monitoring tools. Autonomous Security is intended for teams managing growing AI adoption across employees and devices.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentApply local approval rules before AI agents take risky actions
Inspect and control AI activity on your Mac
Coordinated protection and investigation across enterprise attack surfaces
Manage endpoint and network protection with optional security operations services
Security protection for personal and business devices
Protect home and business devices with malware detection and security controls