Tenable One Cloud Exposure
Find risky cloud configurations, permissions, and vulnerable workloads
Review security risks from application code through cloud runtime
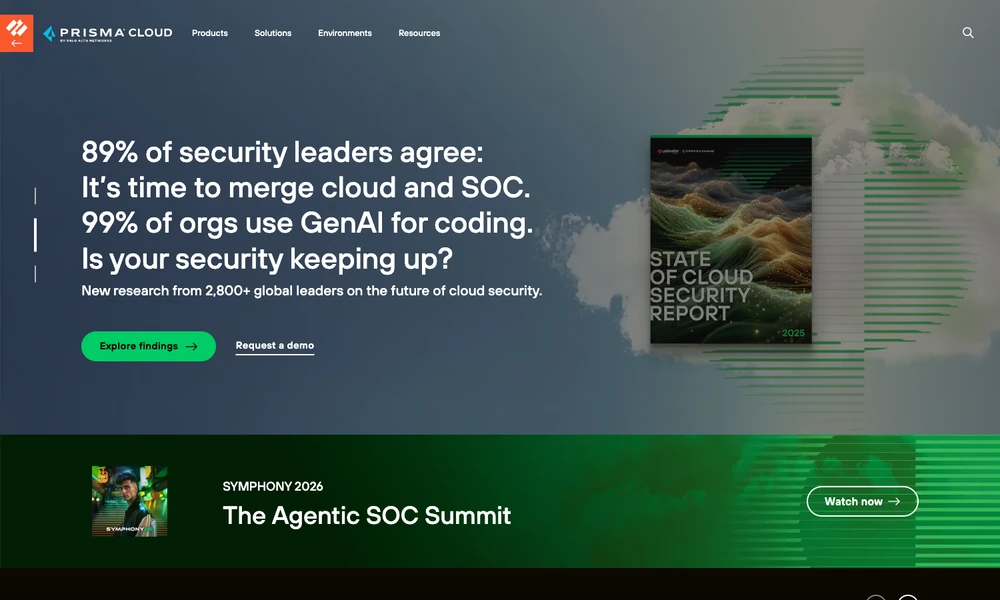
Prisma Cloud examines security across application code, cloud infrastructure, and running workloads. Teams use it to review code flaws, container images, permissions, and runtime activity, connecting findings with the affected resources. Risk prioritization considers how an exposed asset relates to other parts of the environment.
Guided investigation and response tools help analysts follow a finding and decide on a correction. Copilot provides a conversational way to explore the collected information. AI security capabilities add visibility into training data, model integrity, and access to deployed models. The platform supports cloud, multicloud, and hybrid environments, linking development-stage checks with the systems and applications operating in them.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentFind risky cloud configurations, permissions, and vulnerable workloads
Connect cloud risk findings with runtime activity and identity permissions
Cloud security across applications, workloads, and network traffic
Understand risks across cloud environments
Use runtime activity to investigate cloud, container and AI workload risks
Connect cloud risk, code, and runtime security