Burp Suite
Inspect web applications and run manual or automated security tests
Scan code and cloud environments, then review security findings and proposed fixes
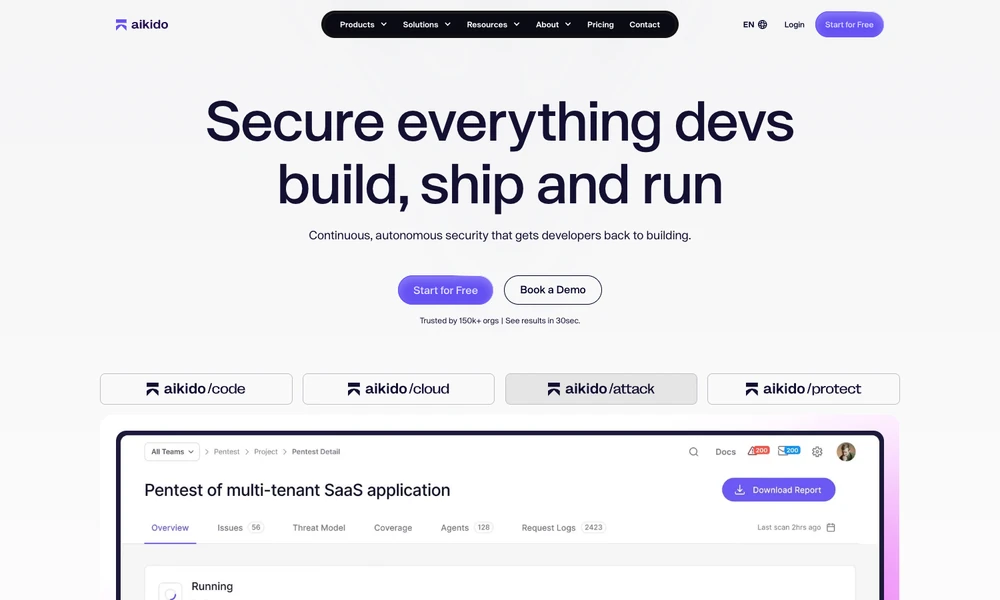
Aikido combines application security checks with tools for investigating and correcting findings. Teams scan code, dependencies, secrets, containers, and infrastructure configuration, then review issues through connected development workflows. Source control, CI, and editor integrations place the findings near the work that may need changing.
AI-assisted fixes can propose code changes for review. Dynamic testing and penetration-testing tools assess running applications, while cloud security examines workloads, permissions, and potential attack paths. Runtime protection adds another layer around application activity. Developers can connect a project, inspect the relevant finding and context, then evaluate the suggested correction alongside the team's other code changes.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentInspect web applications and run manual or automated security tests
Coordinate AI penetration tests and review the evidence in one workspace
Monitor exposed assets and prioritize infrastructure and application vulnerabilities
Arrange scoped security reviews of web applications and APIs with retesting.
Application security checks from source code to running services
Find, prioritize, and remediate risks across the software lifecycle