Burp Suite
Inspect web applications and run manual or automated security tests
Coordinate AI penetration tests and review the evidence in one workspace
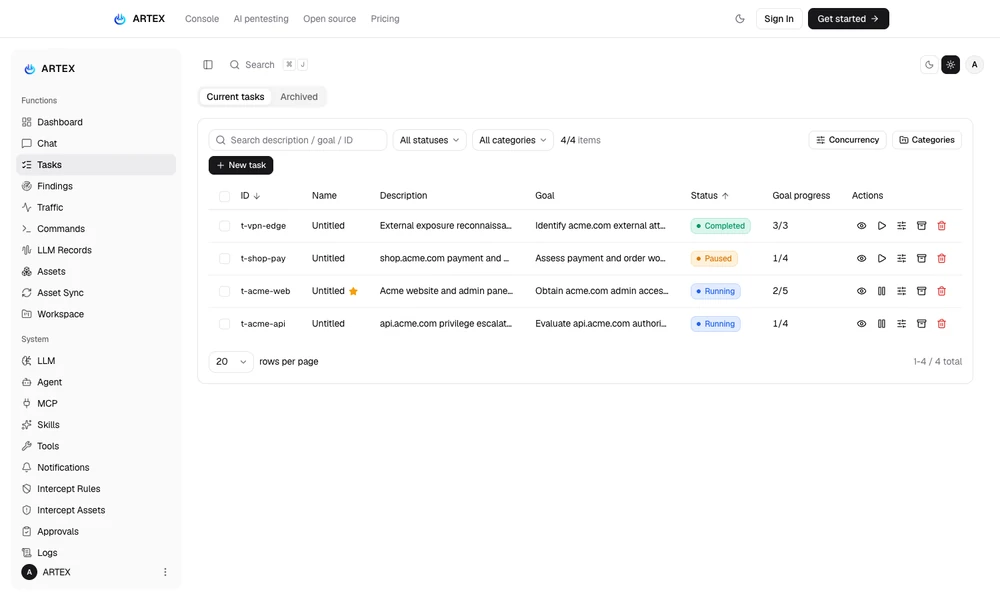
ARTEX is an open-source console for running AI agents through authorized penetration tests. Security teams can define a target and goal, let a planner coordinate parallel workers, and follow progress through a shared view of assets and explored attack paths. Findings stay connected to recorded traffic, commands, and supporting evidence so an operator can inspect what happened.
The workspace brings together task management, model configuration, agent skills, MCP integrations, and approval controls. Teams can review sensitive actions, investigate findings, and run follow-up tests after a fix. ARTEX can be self-hosted as a single application binary or a Docker Compose stack, making it useful for controlled lab assessments and recurring web application or API security work.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentInspect web applications and run manual or automated security tests
Scan code and cloud environments, then review security findings and proposed fixes
Inspect AI agent components for security risks before installation
Arrange scoped security reviews of web applications and APIs with retesting.
Apply rules and human approvals to AI agent actions
Review AI skill repositories with layered security analysis