TRACIO
Use device signals and risk assessments to inform fraud-prevention decisions
Find exposed identities and connect findings to security response
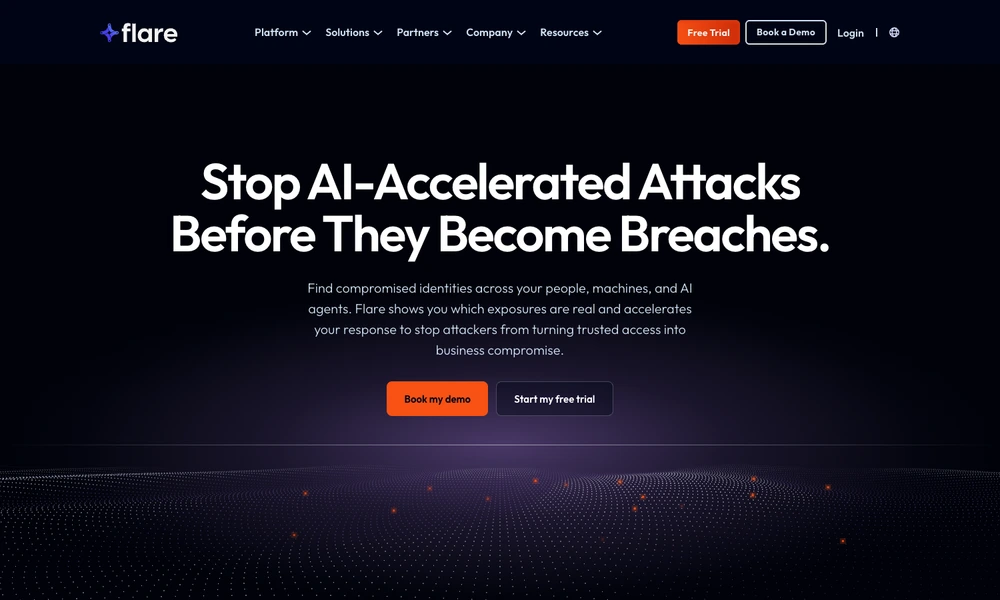
Flare helps security teams find exposed credentials, session cookies, API keys, and other identity information that could provide access to their systems. It monitors sources such as stealer logs, cybercrime forums, messaging channels, and ransomware leak sites, matching findings against the people, domains, and identifiers an organization wants to watch.
Teams can investigate an exposure, check whether access remains active, and connect the finding to response workflows. Integrations with identity providers and security tools support account remediation, alerts, and incident tracking. Flare also supplies threat intelligence feeds and contextual information so analysts can relate an exposed identity to infrastructure, indicators, and wider activity.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentUse device signals and risk assessments to inform fraud-prevention decisions
Check Supabase applications for exposed data and weak access rules
Monitor vendor security signals and organize evidence for risk reviews
Collect security logs, investigate threats, and automate responses
Monitor domain security, email authentication, certificates, and uptime
Identify automated sessions through behavioral analysis