TRACIO
Use device signals and risk assessments to inform fraud-prevention decisions
Check Supabase applications for exposed data and weak access rules
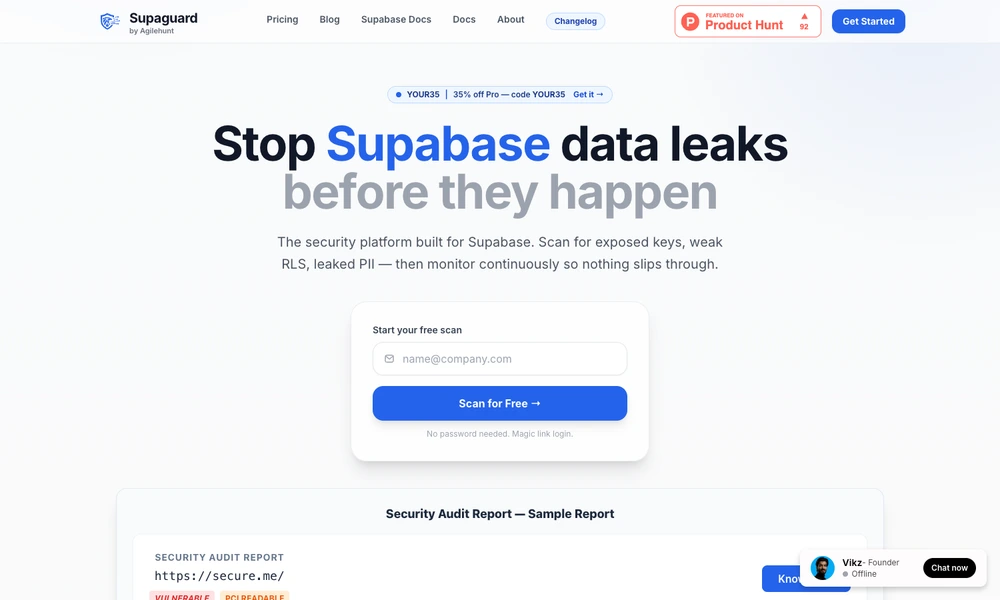
Supaguard checks Supabase-powered applications for exposed credentials, weak row-level security rules, and publicly accessible sensitive data. It examines a site's JavaScript bundles, identifies relevant credentials, and reports which database tables or operations may be reachable through them. Findings are presented in a security report with suggested fixes.
Developers can start with an individual scan or use paid monitoring for multiple projects. Scheduled checks, score history, email alerts, and webhook integrations help teams notice changes over time. The platform also supports deployment-pipeline checks and downloadable reports. Supaguard focuses on the access controls and API behavior of Supabase applications rather than treating every site as the same generic scanning target.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentUse device signals and risk assessments to inform fraud-prevention decisions
Collect security logs, investigate threats, and automate responses
Find exposed identities and connect findings to security response
Protect brand social accounts, permissions, and conversations
Review agent activity and apply explicit controls to tool use
Monitor domain email authentication and investigate unusual senders