ZeroTrusted.ai
Test and govern AI agents with runtime security controls
Connect security findings into testable attack paths and verify fixes
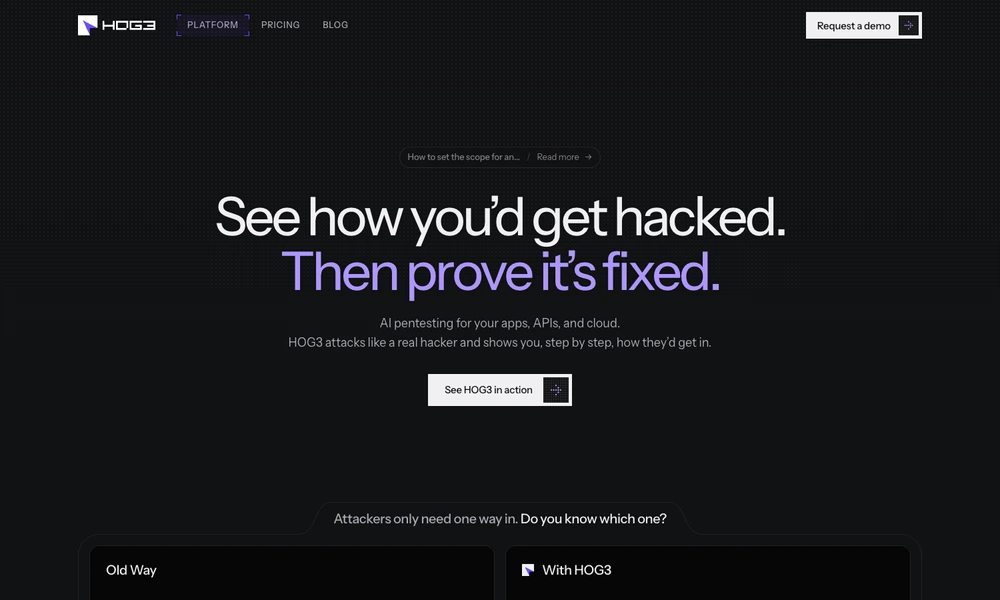
HOG3 provides continuous security testing for applications, APIs, and cloud environments within an agreed testing scope. It maps exposed services and identities, then connects individual weaknesses into attack paths. Findings include supporting evidence and an explanation of the business impact, helping teams understand how a problem could be reached instead of reviewing isolated alerts.
The workflow organizes remediation by the reach of each finding and supplies guidance for the engineers responsible. After a team makes a change, HOG3 repeats the relevant test and keeps the result with the finding. Its commercial plans define the environment and coverage, supporting recurring validation as software changes.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentTest and govern AI agents with runtime security controls
Validate AI responses against configurable safety policies
Coordinate authorized security assessments and review evidence-backed findings.
Apply rules and human approvals to AI agent actions
Review AI skill repositories with layered security analysis
Add runtime security decisions to applications and AI agent actions