Snyk
Find security issues in code and software dependencies
Scan source code for actionable security findings
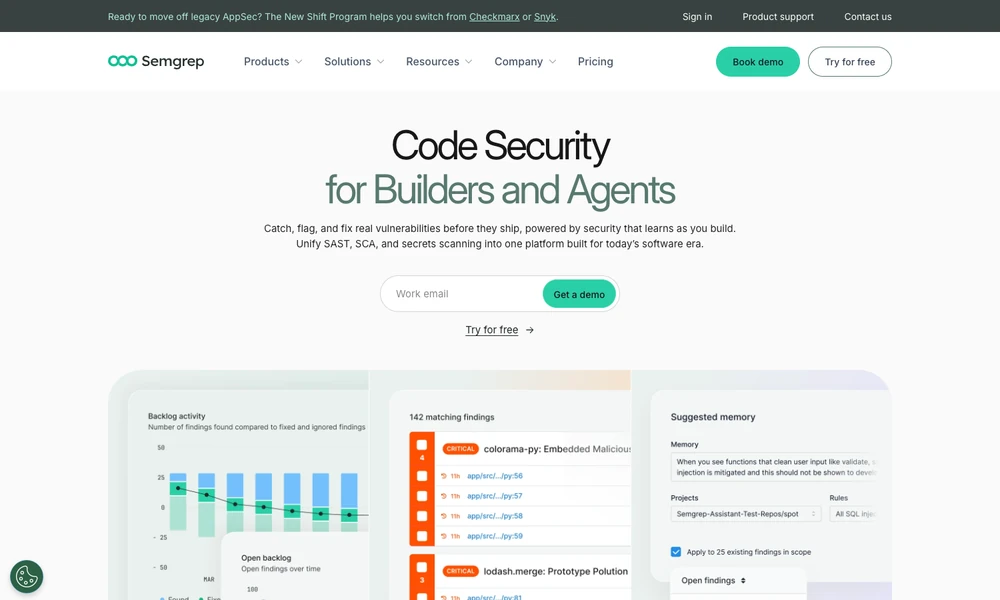
Semgrep scans code, dependencies, and secrets for security issues. Static-analysis rules inspect code patterns, while application context and dependency reachability help prioritize findings. Supply-chain tools also check for malicious open-source packages.
Developers run checks through a CLI, editor, or CI pipeline and receive results in pull requests. Connections include GitHub, GitLab, Bitbucket, and Azure DevOps. AI tools use code context to assist triage, explain a finding, and suggest a change. APIs, webhooks, and ticketing integrations bring the work into the team's review process. Engineers can investigate a reported issue alongside the code and proposed fix before deciding how to address it.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentFind security issues in code and software dependencies
Inspect AI agent components for security risks before installation
Application security checks from source code to running services
Coordinate AI penetration tests and review the evidence in one workspace
Inspect web applications and run manual or automated security tests
Find, prioritize, and remediate risks across the software lifecycle