Squidbrake
Apply rules and human approvals to AI agent actions
Track software dependencies, vulnerabilities, and license risks
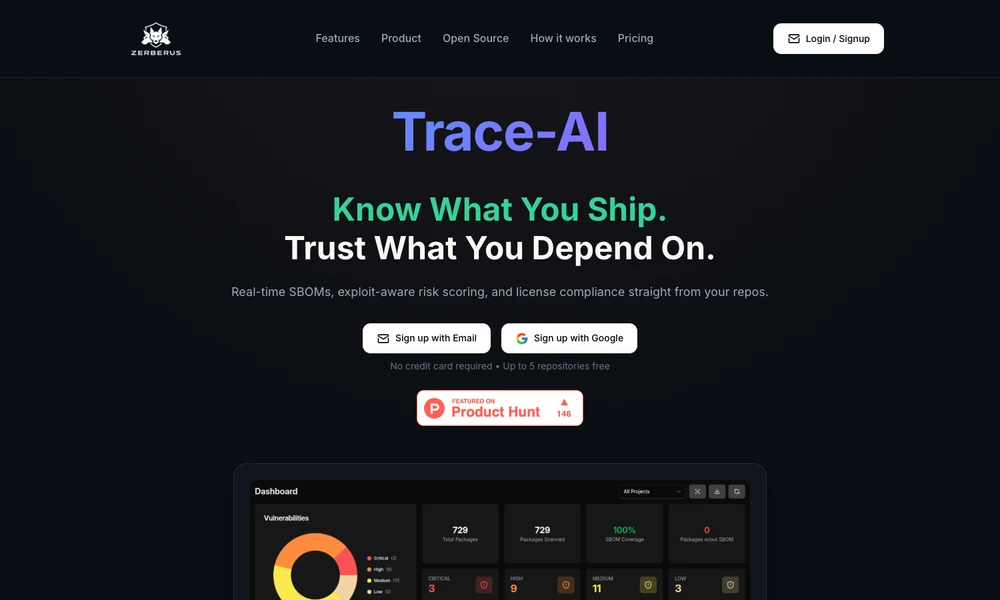
Trace-AI analyzes repository dependency manifests and lock files to create a software bill of materials and track associated risks. Teams connect GitHub or GitLab repositories, inspect direct and transitive dependencies, and review vulnerability and license information in a dashboard. Risk views emphasize exploit context to help prioritize investigation.
The platform also tracks vendor-related information alongside code dependencies and exports evidence in formats including CycloneDX, SPDX, and JSON. Its ZSBOM components publish classification logic and configurable policies for inspection and adaptation. Trace-AI is useful for development and security teams that need a maintained inventory of what their software includes and a clearer basis for reviewing dependency changes.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentApply rules and human approvals to AI agent actions
Review AI skill repositories with layered security analysis
Inspect AI coding traffic through a local security gateway
Continuously test applications and deliver validated security findings and fixes
Inspect published security reports for ClawHub skills before adding them to an agent workflow.
Monitor MCP tools and stop unapproved changes