Sysdig
Use runtime activity to investigate cloud, container and AI workload risks
Apply policies before AI agents act
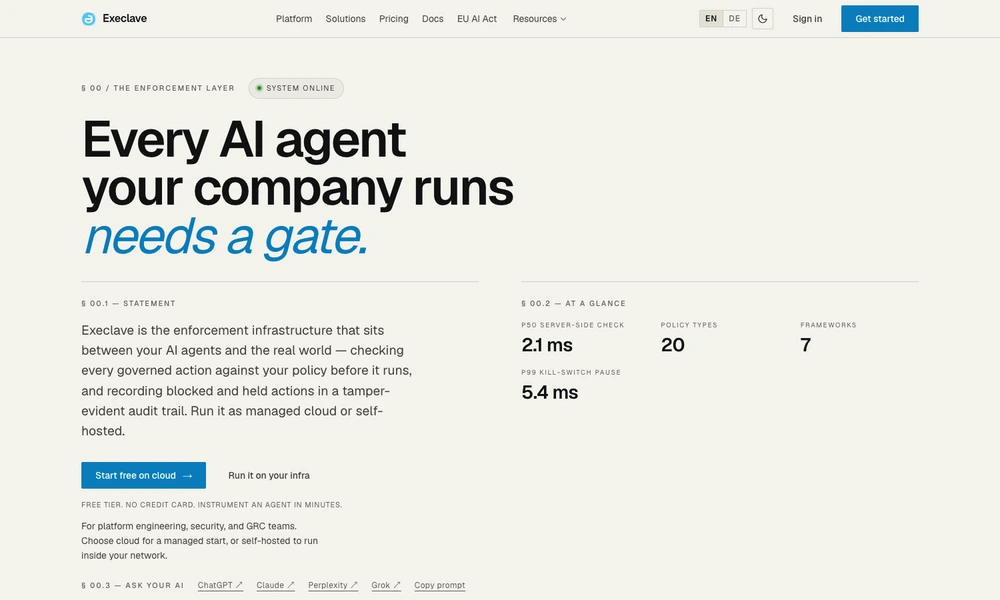
Execlave gives teams a way to control what AI agents can do before their actions reach business systems. Developers place its policy checks before protected operations, then define which requests can proceed, which need human approval, and which should be blocked. The platform records decisions and administrative changes in a tamper-evident audit trail.
Teams can also maintain an agent registry, set spending limits, monitor permission changes, and pause agents through a central control. Execlave offers managed cloud and self-hosted deployment options, making it useful for platform engineers, security teams, and governance staff who need a shared record of agent permissions and activity.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentUse runtime activity to investigate cloud, container and AI workload risks
Understand bot traffic and choose which automated visitors to allow
Discover AI agent connections and apply policies to MCP activity
Compare browser claims with connection measurements to flag suspicious sessions
Apply security controls to live infrastructure access
Find security and infrastructure risks in AWS CDK before deployment