Elastic Security
Investigate threats with security data and automation
Security analytics, threat intelligence, and guided incident response
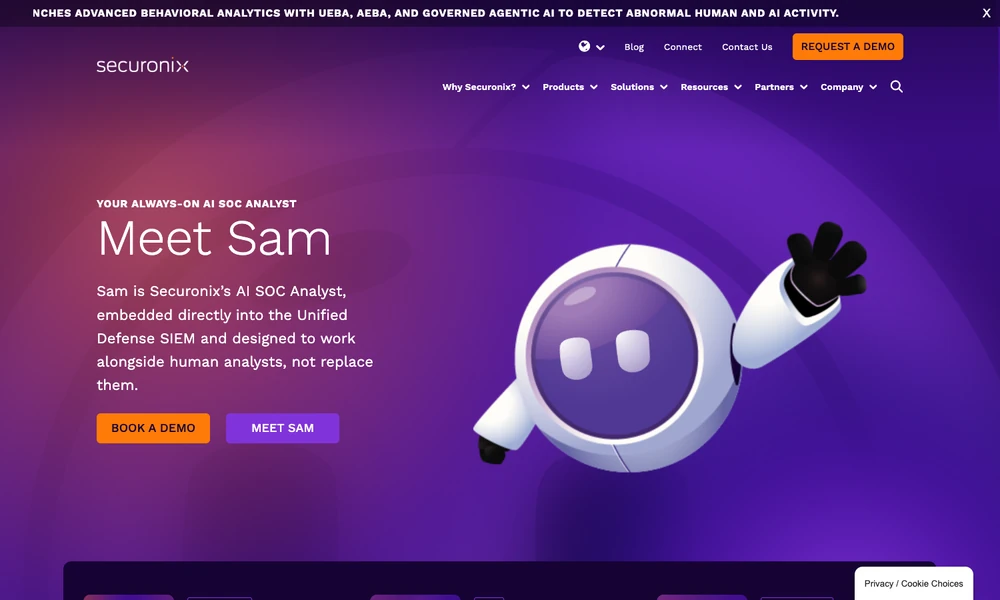
Securonix brings security events, behavioral analysis and threat intelligence into a common investigation workflow. Its Unified Defense platform combines signals from cloud and enterprise systems, using identity and activity context to help analysts examine suspicious behavior. Prebuilt detections and playbooks provide starting points for investigating and responding to a finding.
Sam, the AI SOC analyst, assists with alert triage, enrichment, investigation summaries and case preparation. Analysts can follow the supporting context into a case and coordinate escalation or response, with human oversight of the decisions. Threat-intelligence management and response tools connect that investigation with the wider security team's ongoing monitoring work.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentInvestigate threats with security data and automation
Investigate threats and coordinate security response from shared data
Open-source security monitoring and threat detection
Investigate internet infrastructure through a connected graph of evidence.
Bring multiple threat-intelligence sources into one triage workflow
AI bots that disrupt scams and gather threat intelligence