Elastic Security
Investigate threats with security data and automation
Investigate threats and coordinate security response from shared data
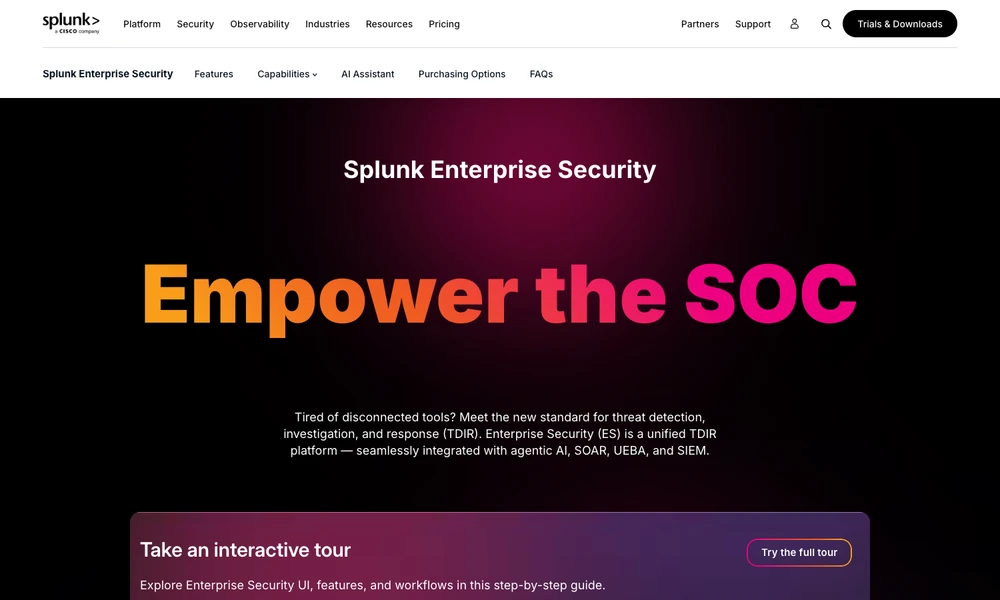
Splunk Enterprise Security connects threat detection, investigation, and response in a security operations workspace. Analysts can search data from different environments, examine related alerts, and prioritize activity using risk context. Detection Studio supports developing and maintaining detection rules as the team's needs change.
AI assistance helps with queries, summaries, and other investigative tasks. Different editions combine SIEM, threat intelligence, automation, and behavioral analytics, with features such as SOAR and user and entity behavior analytics available in selected offerings. Security teams can follow an alert through investigation and response while keeping supporting data and decisions connected, using the tools appropriate to their environment and edition.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentInvestigate threats with security data and automation
Security analytics, threat intelligence, and guided incident response
Bring multiple threat-intelligence sources into one triage workflow
Open-source security monitoring and threat detection
Connect endpoint and identity signals to investigation and response workflows
Investigate and respond to endpoint, identity and cloud threats through Falcon