Splunk Enterprise Security
Investigate threats and coordinate security response from shared data
Investigate threats with security data and automation
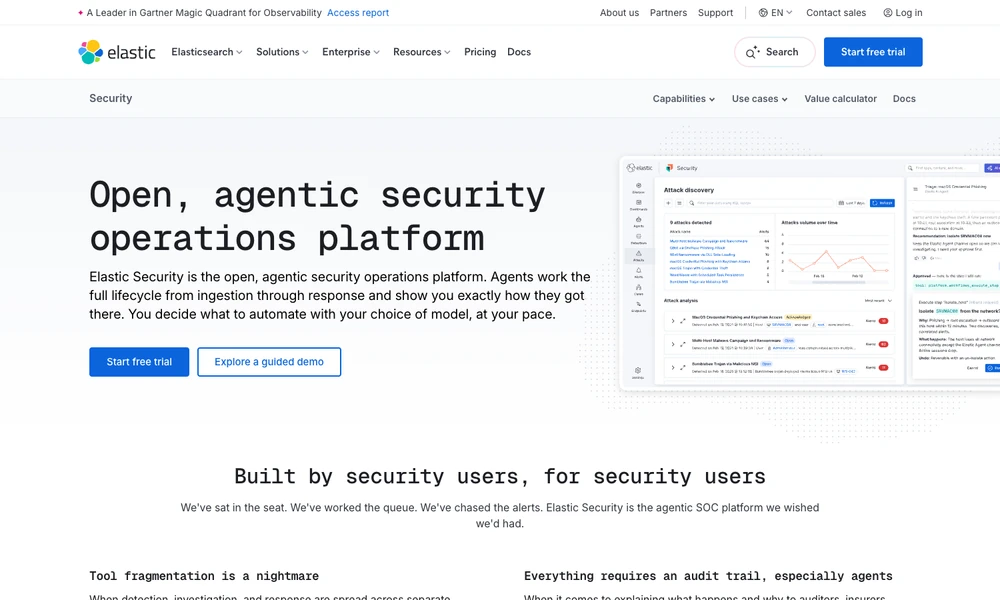
Elastic Security connects security data, detections, and investigation tools. Integrations normalize incoming information, with dashboards providing a starting point for examining a source. Published detection rules let teams read the logic behind an alert and adapt it to their environment.
Search and correlation bring related events into an investigation. Attack Discovery can connect alerts into attack chains and show the activity behind the conclusion, while response workflows carry findings toward action. Endpoint protections and automated tools sit alongside that analysis. Analysts can inspect the supporting records and tune rules before using those results in their incident-response process.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentInvestigate threats and coordinate security response from shared data
Open-source security monitoring and threat detection
Security analytics, threat intelligence, and guided incident response
Connect endpoint and identity signals to investigation and response workflows
Investigate and respond to endpoint, identity and cloud threats through Falcon
Use a managed security team for detection, investigation and remediation