Otter Vault
Save one-time API keys in an encrypted browser vault
Manage application secrets with machine identity and granular access policies
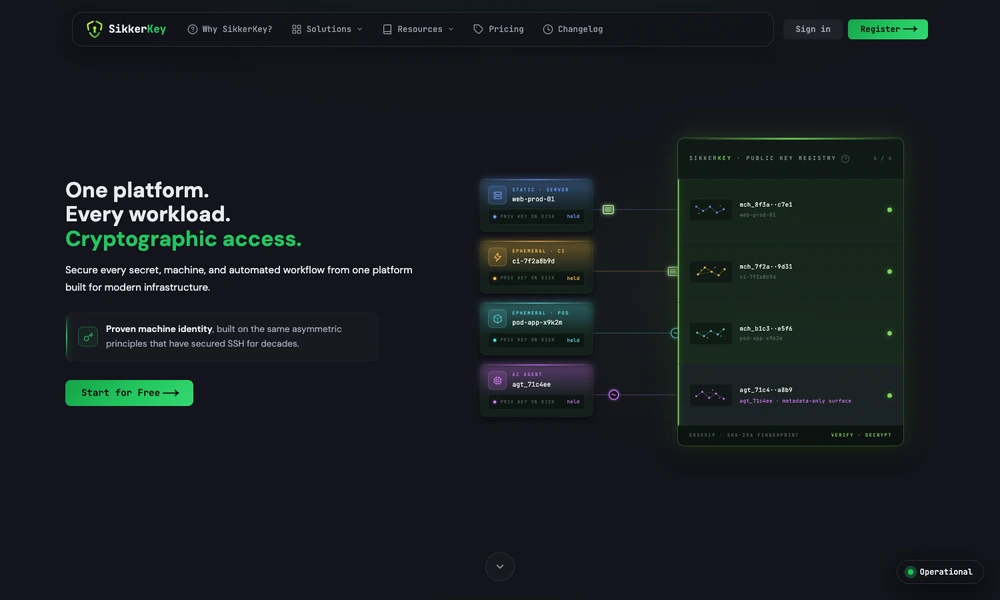
SikkerKey stores application credentials in an encrypted vault and controls which machines can retrieve them. Its authentication model uses public and private keys, allowing servers, containers, CI jobs, and other workloads to identify themselves without relying on a shared vault password. SDKs, a command-line tool, and an HTTPS API support integration.
Access policies can combine network restrictions, time windows, rate limits, and approval requirements. Teams can inspect versions and read history, rotate credentials, and configure decoy secrets that trigger a response when accessed. AI integrations can help manage vault metadata and policies while keeping the capability to read actual secret values separate.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentSave one-time API keys in an encrypted browser vault
Manage secrets and temporary access for machines, people and AI agents
Connect your accounts to AI assistants with scoped permissions.
Detect and redact exposed credentials before pasting into AI tools
Issue and manage application secrets, certificates and encryption keys
Store infrastructure secrets and scope access for machines and teams