HashiCorp Vault
Issue and manage application secrets, certificates and encryption keys
Manage secrets and temporary access for machines, people and AI agents
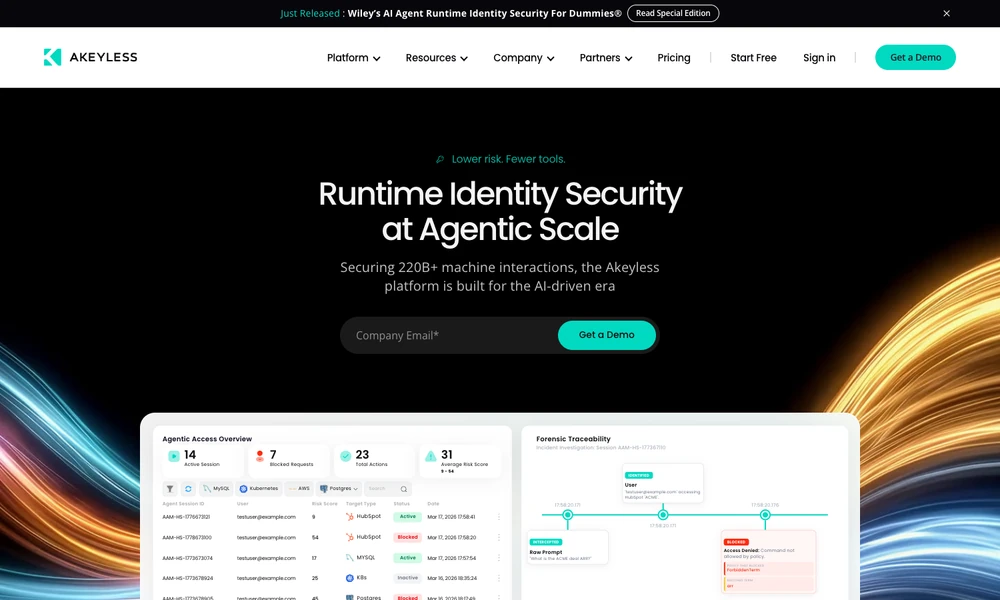
Akeyless manages secrets, certificates, encryption keys, and access identities across infrastructure. Authorized workloads obtain credentials through the secrets service, while privileged-access tools give people time-limited access to systems. Certificate management covers issuance and renewal within the same broader platform.
A shared policy engine connects controls for human users, machines, and AI agents. Runtime identity tools scope agent activity, and multi-vault governance connects existing secret stores rather than requiring immediate replacement. Teams can define access for a particular workload or operation and review the relevant identities and permissions. Multi-cloud key management extends those workflows to encryption keys used across connected environments.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentIssue and manage application secrets, certificates and encryption keys
Store infrastructure secrets and scope access for machines and teams
Open-source secrets storage, dynamic credentials, and encryption services
Manage application secrets with machine identity and granular access policies
Manage secrets and machine access in one platform
Manage application secrets across development, deployment and AI-agent workflows