Akeyless
Manage secrets and temporary access for machines, people and AI agents
Issue and manage application secrets, certificates and encryption keys
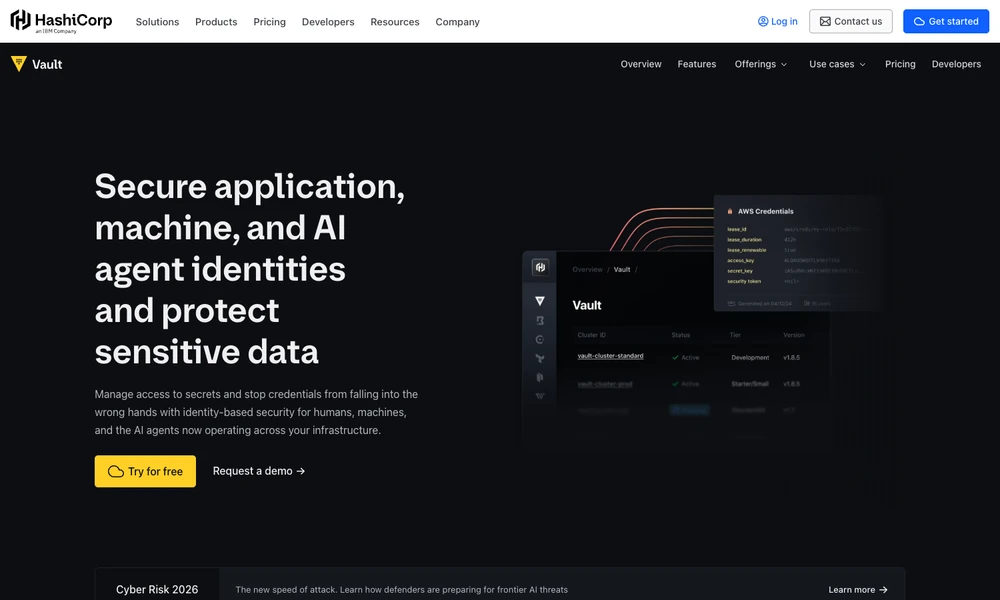
HashiCorp Vault manages access to secrets through identity-based policies. Applications, services, people, and AI agents request credentials programmatically, with authorization rules determining what each identity can receive. Secrets, certificates, and encryption keys can be managed in the same system.
Lifecycle tools cover generating, rotating, expiring, and revoking access. Encryption services let applications work with protected data without placing the underlying keys in their own code. A workload can receive temporary database credentials governed by a policy, while administrators maintain the rules centrally and use the API to automate the related credential tasks.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentManage secrets and temporary access for machines, people and AI agents
Store infrastructure secrets and scope access for machines and teams
Open-source secrets storage, dynamic credentials, and encryption services
Manage secrets and machine access in one platform
Manage and distribute application secrets
Manage application secrets with machine identity and granular access policies