SentinelOne
Connect endpoint and identity signals to investigation and response workflows
Investigate and respond to endpoint, identity and cloud threats through Falcon
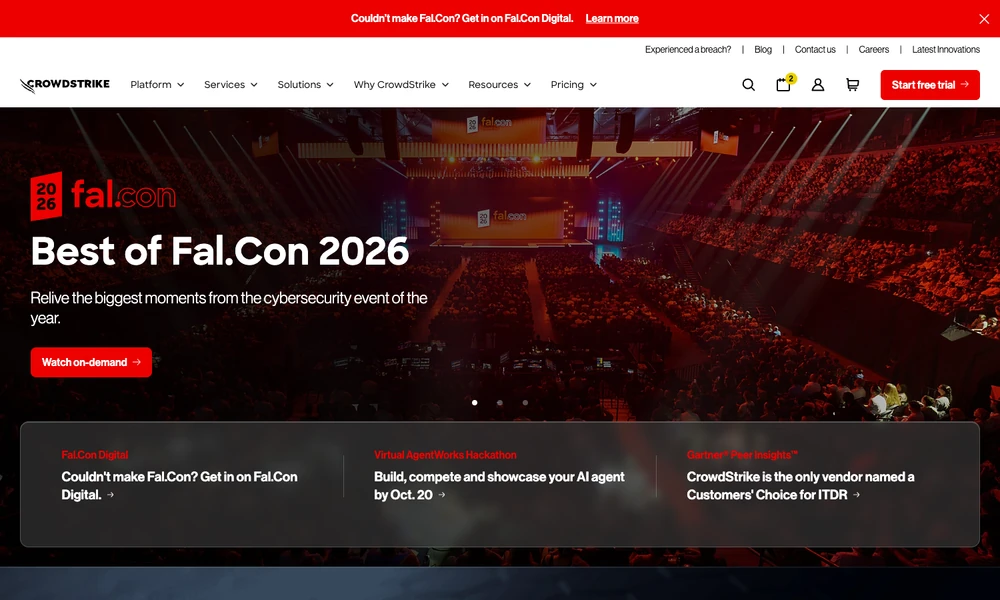
CrowdStrike's Falcon platform connects endpoint protection, threat intelligence, and security operations. Available modules include antivirus, device control, endpoint detection and response, identity protection, and cloud security. Organizations choose the tools appropriate to their devices, workloads, and accounts.
SIEM capabilities analyze security logs, while managed detection and response adds specialists to operational monitoring and investigation. Security teams can examine suspicious activity using the collected context and threat information, then coordinate the response through the platform's tools. Bundles and additional modules determine coverage and service responsibilities, allowing an organization to combine internal security work with selected managed services.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentConnect endpoint and identity signals to investigation and response workflows
Use a managed security team for detection, investigation and remediation
Bring multiple threat-intelligence sources into one triage workflow
Investigate threats and coordinate security response from shared data
Investigate threats with security data and automation
Open-source security monitoring and threat detection