Huntress
Use a managed security team for detection, investigation and remediation
Connect endpoint and identity signals to investigation and response workflows
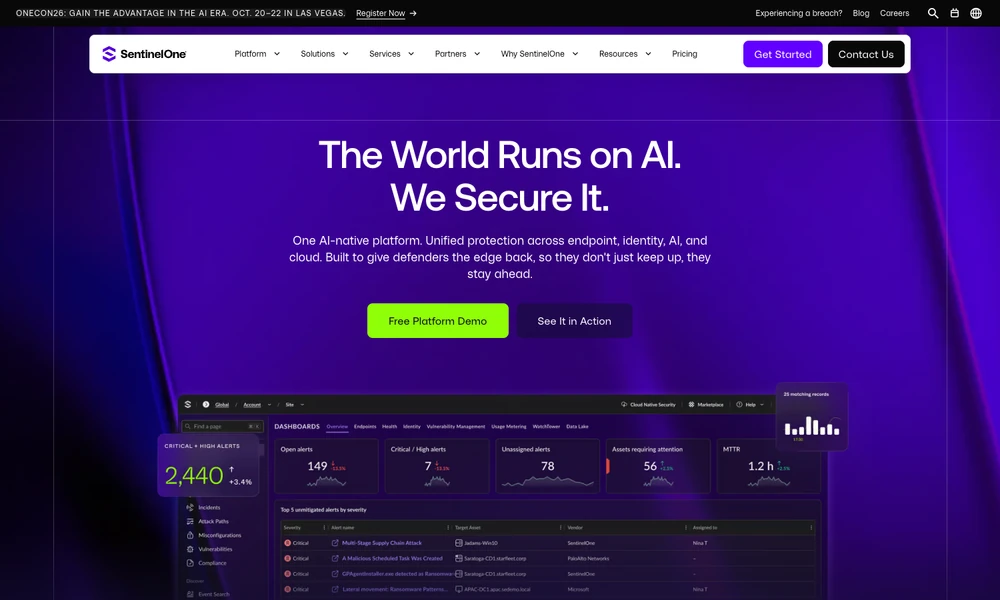
SentinelOne combines endpoint, identity, cloud, and AI security information in a shared platform. Device agents and connected systems supply activity for detecting and investigating suspicious behavior. Analysts use a common console to review findings, correlate events, and coordinate containment or remediation.
Purple AI and agent workflows assist with triage, investigation questions, and routine response tasks. The Security Data Lake brings additional security records into the analysis, while deployment choices include hosted, on-premises, hybrid, and disconnected environments. A team can move from an endpoint or identity alert to its related events and response actions, using the configuration suited to the systems it operates.
Tried it? Share a useful thought or ask a question.
Good conversations start with a hello.
Sign in to commentUse a managed security team for detection, investigation and remediation
Investigate and respond to endpoint, identity and cloud threats through Falcon
Bring multiple threat-intelligence sources into one triage workflow
Investigate threats and coordinate security response from shared data
Investigate threats with security data and automation
Open-source security monitoring and threat detection